036, 037, 067, 137, 167
The NEW YORK MASTERLIST
OCTOBER-10, 2026
CODES 157, 158, 169
028 029 034 035 036 037 046 056
066 067 078 079 128 129 134 135
136 137 146 156 166 167 178 179
REDUCED
034 035 036 037 046 067 134
135 137 156 167 178 179 (13)
===================================
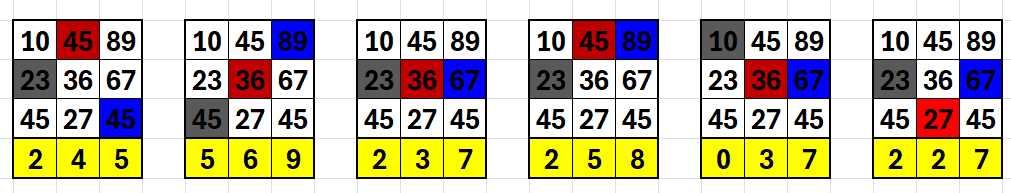
10-45-89 REPEATS
4-Way Match: 245 345 456 457 (4)
3-Way Match: 246 247 256 257 346 347 356 357 445 455 (10)
2-Way Match: 045 046 047 056 057 067 145 146 147 156 157 167 234 235 236 237 238 239 244 248 249 255 258 259 267 344 348 349 355 358 359 367 446 447 458 459 467 556 557 567 (40)
========================================
REPEATS–54
045 046 047 056 057 067 145 146 147 156 157 167 234 235 236 237 238 239 244 245 246 247 248 249 255 256 257 258 259 267 344 345 346 347 348 349 355 356 357 358 359 367 445 446 447 455 456 457 458 459 467 556 557 567 (54)
EVENING–246 247 256 259
=======================================
MAGIC-56
036 037 038 039 046 047 048 049
056 057 058 059 067 068 069 136
137 138 139 146 147 148 149 156
157 158 159 167 168 169 236 237
238 239 246 247 248 249 256 257
258 259 267 268 269 346 347 348
349 356 357 358 359 367 368 369
REDUCED–2-Way Match: 036 037 038 039 048 059 067 069 136 138 146 148 156 157 158 159 167 168 169 236 237 238 239 246 247 248 249 259 267 269 348 358 359 367 368 369 (36)
=================================
036 037 039 068 069 258 268 348 (8)
===============================
Doubles
044 055 066 077 144 155 166 177 224 225 226 227 228 229 244
255 266 277 334 335 336 337 338 339 344 355 366 377 445 446
447 448 449 455 466 477 556 557 558 559 566 577 (42)
Triples
444 555 (2)
===============================
=================================
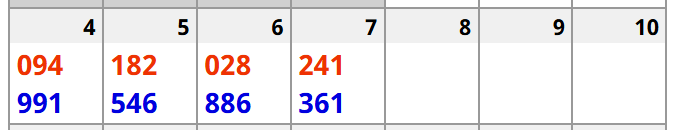
361 241 886 028 546 182 991 094 857 477 856 021 646 701 225 729 219 912 473 613 782 980 043 503 358 898 630 039 351 201 956 764 046 562 607 936 980 926 309 263 197 722 730 258 273 965 524 697 553 340 015 097 991 655 037 116 015 310 104 655 682 343 090 077 086 438 630 886 116 394 913 468 609 748 664 115 096 147 842 659 648 843 768 078 068 907 863 682 681 829 485 765 571 558 241 975 907 225 290 403 415 582 952 003 429 485 225 493 021 880 128 057 014 557 117 254 191 273 852 379 448 638 732 408 325 491 185 091 070 873 558 246 078 555 276
===============================
============================
CHATGPT-STRT
$9–Straight List–https://www.paypal.com/ncp/payment/VRQYFNX5S7U38
Pairs 36-39-69 Playlist
036 039 069 136 139 169 236
239 269 336 339 346 349 356
359 366 367 368 369 379 389
399 469 569 669 679 689 699 (28)
Singles
036 039 069 136 139 169 236
239 269 346 349 356 359 367
368 369 379 389 469 569 679
689 (22)
Doubles
336 339 366 399 669 699 (6)
============================
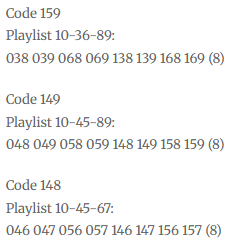
158 FOLLOWERS-148, 159, 248
159 FOLLOWERS-259, 148, 149
157-FOLLOWERS-159, 258, 349
359-FOLLOWERS-249, 149, 159
============================
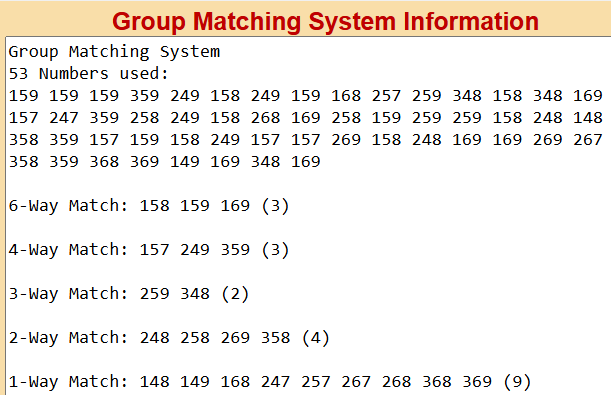
33-Way Match: 149 (1)
31-Way Match: 159 (1)
30-Way Match: 249 (1)
28-Way Match: 148 (1)
20-Way Match: 169 248 (2)
17-Way Match: 158 258 349 (3)
16-Way Match: 348 359 (2)
15-Way Match: 259 (1)
13-Way Match: 269 (1)
11-Way Match: 157 168 257 369 (4)
10-Way Match: 147 358 (2)
9-Way Match: 247 (1)
8-Way Match: 167 (1)
5-Way Match: 268 (1)
4-Way Match: 267 (1)
3-Way Match: 368 (1)
1-Way Match: 347 (1)
============================
STRAIGHT
080 081 084 085 090 091 094 095
180 181 184 185 190 191 194 195
686 687 696 697 786 787 796 797
880 881 890 891 980 981 990 991 (32)
============================
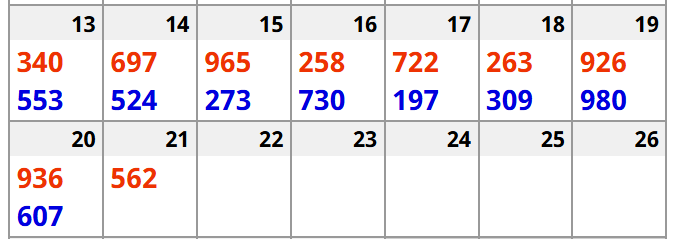
562 607 936 980 926 309 263 197 722 730 258 273 965 524 697 553 340 015 097 991 655 037 116 015 310 104 655 682 343 090 077 086 438 630 886 116 394 468 913 748 609 664 115 096 147 842 659 648 843 768 078 068 907 863 682 681 829 485 765 571 558 241 975 907 225 290 403 415 582 952 003 429 485 225 523 021 880 493 128 057 014 557 117 254 191 273 852 379 448 638 732 408 325 491 185 091 070 873 558 246 078 555 276 848 243 983 023 061 502 168 888 132 261 911 435 832 963 861 540 535 400 338 635 371 760 973 084 170 098 507 527 419 295 600 809 800 976 319 140 580 747 283 056 979 204 839 020 380 222 686 853 698 040 446 438 471 317 489 536 182 884 206 301 925 401
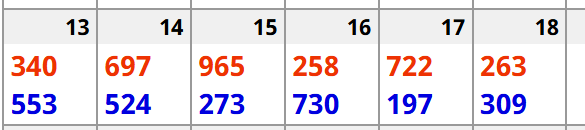
========================
2026–STARTING FROM JANUARY-1
117 174 998 256 243 679 793 489 080 735 181 342 916 286 199 732 989 835 052 456 992 091 924 586 009 018 519 402 901 684 539 496 904 285 682 094 769 440 479 406 616 233 981 787 389 771 716 551 977 183 076 866 517 065 090 733 152 592 123 415 117 732 816 061 475 945 815 379 021 547 480 759 166 591 748 983 485 734 646 394 073 570 119 909 866 635 121 117 942 548 687 759 423 233 578 231 954 428 501 768 417 337 707 957 653 053 426 140 585 902 999 566 925 727 262 440 360 722 133 089 543 917 632 094 318 270 129 447 134 053 087 651 100 147 900 298 119 082 370 147 354 865 340 986 495 723 812 801 159 797 829 744 578 299 303 047 401 055 271 899 892 618 939 409 539 153 575 673 904 479 797 463 562 693 304 508 091 246 581 890 013 824 881 741 956 119 169 292 090 838 238 519 279 236 116 736 365 132 433 789 756 983 598 216 775 458 460 381 123 333 825 793 604 270 685 890 945 387 681 018 718 464 690 156 985 470 195 055 080 095 710 254 090 287 537 058 052 224 491 876 903 724 066 586 458 931 294 892 531 745 319 402 614 161 397 717 732 796 211 657 533 599 096 846 003 465 113 228 905 169 391 781 999 981 480 605 293 787 272 992 931 529 687 178 175 670 357 133 665 784 890 763 100 200 088 458 827 940 783 194 764 816 536 447 033 596 075 348 481 904 019 955 816 814 913 926 395 679 817 452 993 189 330 539 324 747 449 392 330 657 149 381 876 840 868 097 085 335 787 611 176 670 039 465 750 771 084 515 828 430 958 723 061 575 704 116 457 054 536 542 658 522 401 925 301 206 884 182 536 489 317 471 438 446 040 698 853 686 222 380 020 839 204 979 056 283 747 580 140 319 976 800 809 600 295 419 527 507 098 170 084 973 760 371 635 338 400 535 540 861 963 832 435 911 261 132 888 168 502 061 023 983 243 848 276 555 078 246 558 873 070 091 185 491 325 408 732 638 448 379 852 273 191 254 117 557 014 057 128 493 880 021 523 225 485 429 003 952 582 415 403 290 225 907 975 241 558 571 765 485 829 681 682 863 907 068 078 768 843 648 659 842 147 096 115 664 609 748 913 468 394 116 886 630 438 086 077 090 343 682 655 104 310 015 116 037 655 991 097 015 340 553 697 524 965 273 258 730 722 197 263 309 926 980 936 607 562 046 764 956 201 351 039 630
=================================
KEY-4 REDUCED with the RUNDOWN LIST
045 046 047 048 049 146 148
149 246 247 249 345 346 347 (14)
==========================
47 HOTTEST CODES
112 114 121 124 131 135 141 142 143 151
152 153 155 224 225 233 235 253 255 311
312 321 322 323 324 331 341 353 355 411
412 423 424 434 442 452 454 514 532 533
542 543 544 545 551 554 555 (47)
=========================
32-Way Match: 245 (1)
31-Way Match: 124 135 (2)
28-Way Match: 235 (1)
25-Way Match: 123 134 (2)
24-Way Match: 125 234 (2)
22-Way Match: 345 (1)
=========================
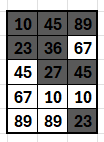
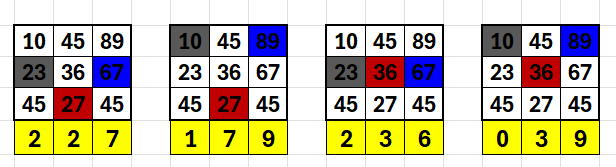
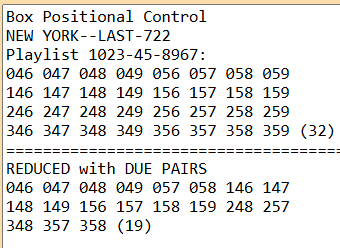
REDUCED with DUE PAIRS
046 047 048 049 057 058 146 147
148 149 156 157 158 159 248 257
348 357 358 (19)
====================================
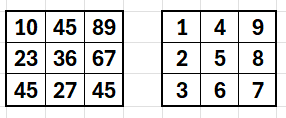
Box Positional Control
NEW YORK–LAST-722
Playlist 1023-45-8967:
046 047 048 049 056 057 058 059
146 147 148 149 156 157 158 159
246 247 248 249 256 257 258 259
346 347 348 349 356 357 358 359 (32)
=================================
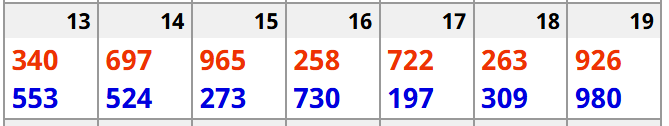
980 926 309 263 197 722 730 258 273 965 524 697 553 340 015 097 991 655 037 116 015 310 104 655 682 343 090 077 086 438 630 886 116 394 468 913 748 609 664 115 096 147 842 659 648 843 768 078 068 907 863 682 681 829 485 765 571 558 241 975 907 225 290 403 415 582 952 003 429 485 225 523 021 880 493 128 057 014 557 117 254 191 273 852 379 448 638 732 408 325 491 185 091 070 873 558 246 078 555 276 848 243 983 023 061 502 168 888 132 261 911 435 832 963 861 540 535 400 338 635 371 760 973 084 170 098 507 527 419 295 600 809 800 976 319 140 580 747 283 056 979 204 839 020 380 222 686 853 698 040 446 438 471 317 489 536 182 884 206 301 925 401
===================================
Straight Positional Control-STRAIGHT
Playlist 102345-453627-896745:
024 025 026 027 028 029 034 035 036 037 038 039 044 045 046 047 048 049 054 055 056 057 058 059 064 065 066 067 068 069 074 075 076 077 078 079 124 125 126 127 128 129 134 135 136 137 138 139 144 145 146 147 148 149 154 155 156 157 158 159 164 165 166 167 168 169 174 175 176 177 178 179 224 225 226 227 228 229 234 235 236 237 238 239 244 245 246 247 248 249 254 255 256 257 258 259 264 265 266 267 268 269 274 275 276 277 278 279 324 325 326 327 328 329 334 335 336 337 338 339 344 345 346 347 348 349 354 355 356 357 358 359 364 365 366 367 368 369 374 375 376 377 378 379 424 425 426 427 428 429 434 435 436 437 438 439 444 445 446 447 448 449 454 455 456 457 458 459 464 465 466 467 468 469 474 475 476 477 478 479 524 525 526 527 528 529 534 535 536 537 538 539 544 545 546 547 548 549 554 555 556 557 558 559 564 565 566 567 568 569 574 575 576 577 578 579 (216)
BOTH–024 025 026 027 028 038 045 046 047 048 049 054 057 064 067 074 075 076 125 126 134 135 136 138 146 148 156 158 159 164 165 167 169 176 234 238 246 247 249 257 264 267 274 275 276 324 328 345 346 347 354 357 358 364 367 374 375 376 378 426 427 429 435 436 437 457 467 475 476 527 534 537 538 547 574 578 (76)
RUNDOWN-2WAY–STRAIGHT #S
2-Way Match: 024 025 026 027 028 035 038 045 046 047 048 049 054 056 057 058 059 064 065 067 074 075 076 125 126 127 128 129 134 135 136 137 138 146 148 149 156 158 159 164 165 167 169 176 178 234 235 238 239 246 247 249 256 257 264 265 267 274 275 276 278 279 324 325 328 329 345 346 347 354 356 357 358 359 364 365 367 369 374 375 376 378 379 426 427 429 435 436 437 456 457 459 465 467 469 475 476 479 526 527 534 536 537 538 539 546 547 549 564 568 574 578 (112)
DUE REDUCED PAIRS
2-Way Match: 024 025 026 027 028 029 034 038 044 045 046 047 048 049 054 057 064 067 074 075 076 124 125 126 134 135 136 138 145 146 148 154 155 156 157 158 159 164 165 166 167 168 169 175 176 224 234 238 244 245 246 247 248 249 254 257 264 267 274 275 276 324 328 334 338 344 345 346 347 348 349 354 357 358 364 367 368 374 375 376 378 424 425 426 427 428 429 434 435 436 437 438 439 448 457 458 467 468 475 476 478 524 527 534 537 538 547 548 557 567 574 575 576 577 578 579 (116)
==================================
=====================================
012 013 014 015 016 017 018 019 023 024
025 026 027 028 029 034 035 036 037 038
039 045 046 047 048 049 056 057 058 059
067 068 069 078 079 089 123 124 125 126
127 128 129 134 135 136 137 138 139 145
146 147 148 149 156 157 158 159 167 168
169 178 179 189 234 235 236 237 238 239
245 246 247 248 249 256 257 258 259 267
268 269 278 279 289 345 346 347 348 349
356 357 358 359 367 368 369 378 379 389
456 457 458 459 467 468 469 478 479 489
567 568 569 578 579 589 678 679 689 789
=====================================
=================================

====================================================
NEW YORK
https://www.lotterypost.com/results/ny/win4/calendar/2026
July 9, 2026
1085 4830 4795 4501 6883 1932 7355 0042 4856 6740 2536 7606 6378 1117 6086 7653 5736 6482 2435 3435 4557 0872 3820 2164 1508 9275 1642 6664 6193 2000 5640 2167 5665 7031 4405 4416 9932 1910 2627 4088 7362 4564 0599 0669 5231 7942 3219 9616 2102 9338 0092 8297 0785 0286 8669 4789 5248 3315 7842 0800 1498 6071 2093 5180 2607 1619 4085 6868 1773 4028 8187 2560 6512 3066 9374 1657 4208 7739 8640 7563 7622 5280 4234 1473 5487 2795 9492 1342 1063 1163 2485 7578 6815 7749 7603 9908 7267 9551 7339 9905 9234 7163 7294 2709 9639 9554 4092 2746 2930 6050 4158 3616 7017 3691 2216 0884 2400 5757 9104 9076 5598 5163 1823 4888 9673 1792 1918 1059 2653 5954 7556 4734 7205 5328 5166 5751 1680 1779 1632 7865 4204 1957 8723 9404 6662 4038 0641 2243 8244 6708 3825 3392 4965 5360 7657 6200 9950 3867 4419 6123 8956 9597 2092 1033 7843 7403 2100 5081 6976 9481 9708 4542 4630 2507 1595 7305 8531 7888 4918 8093 7189 0852 8448 2022 8158 6222 0699 8447 3832 3330 3605 8940 2725 4073 8921 5624 6224 7633 9681 0503 1730 9155 5826 2378 3229 0220 4656 1671 0261 6850 1391 5823 5269 3094 2561 4609 7956 0781 0783 4513 2193 7486 0565 5470 8166 1392 8960 7206 8102 4391 4407 2360 6276 7295 6031 5681 7879 1698 5354 8561 3654 1936 1105 5073 4408 7330 7653 8908 4302 5164 0283 3559 8681 6139 8896 5214 6212 5734 4686 8572 7358 7875 5076 4256 6506 6155 2002 8704 8691 4656 4854 1253 8076 5255 8686 9837 8122 8515 5076 8396 2294 6903 8244 7213 4035 8217 4254 1925 5575 5758 8820 8911 6175 7515 7465 3681 8106 8383 2771 8548 1849 0633 2686 3466 9363 4325 6184 4684 3326 7183 1333 1330 9474 2647 5330 3962 1465 1220 1977 5964 2968 8188 2006 3391 7906 1044 0495 1550 9094 5395 1673 9983 1960 7376 8035 0814 0077 2444 2616 9347 0047 0905 1959 3971 9195 1501 9988 0804 8072 8350 3889 0617 9719 6250 8340 1172 9544 4945 2926 2990 9493 4707 1090 0945 6957 6729 5927 6118 4424 2666 8223 8363 6731 8404 1279 4540 8049 3630 3317 5546 3796 2328 3503 9488 1372 7337 4295 0985 2919 0705 2600 4573 7373 0334 0640 1922 7643 6223 2919 5082 1601 9620 1502 1141 6144 8650 3308 1902 0930 0143 0868 2128 0271 9114 8858 3209 3588 9192 0175 0554 2291 4264 1503 8145 9974 2639 3875 9378 5013 0115 5676 7821 5748 8476 9328 9647 5848 4981 6873 4195 3231 9283 2686 8277 7534 9055 8911 3714 9969 8270 4307 5597 2440 5763 7019 5931 8491 7850 8527 8315 3098 0306 1476 7236 2666 3353 5466 4470 0979 2284 7488 0105 8312 4244 7094 9200 6498 0203 4924 8243 7813 0683 3997 2384 1486 7322 2303 5164 0723 3721 8824 2110 0302 0483 1943 4431 0402 0197 3838 7597 4480 1690 4629 0512 4459 9960 4288 9154 7269 1193 1556 2842 5202 5772 0254 1004 2310 9979 9536 9348 4633 5736 6856 2574 8831 5877 0282 1616 0090 9387 0648 1850 7584 9142 6486 6500 5044 0238 4246 5242 5692 1307 9827 1001 0129 5066 6158 3611 0494 3072 9647 4864 3290 7642 7716 6114 1644 2052 6454 3568 6933 2846 9928 5741 2114 8852 5386 7466 1950 3447 9986 5734 0570 2286 0144 6727 7821 4797 2980 8245 9037 7386 3969 4036 4292 8732 1061 7699 9897 0373 3164 0639 6702 0512 3481 7863 1559 3728 8424 6011 8553 0040 3457 9065 6060 1740 1070 5867 7573 6378 7791 2488 6117 2384 2106 8518 6959 9638 3403 7950 5443 8984 0303 9387 3869 4227 8746 1191 1305 6646 4564 7328 2131 3408 2180 3420 1984 2284 8527 7648 5539 7217 2468 9820 6538 2579 3184 6286 6689 7310 5712 2770 9724 2416 0905 0098 4372 8798 6543 8419 7915 2581 3869 1390 2449 9688 5778 2909 1564 1093 0076 5160 3272 5281 1520 7460 8791 0845 8122 7073 4859 3369 9840 0299 3942 5630 8873 1872 4643 0975 9025 7991 8924 5152 1765 1649 7084 4253 1001 1037 9828 6389 0048 8474 4323 6275 3098 1658 5805 2149 8440 1930 1173 3715 1939 5867 8927 0981 3903 0947 0643 8582 2402 4290 4337 5195 8579 4106 4589 4634
==============================
===============================
PROG–5AM to 9AM—4 HOURS
===============================
==================================
============================
BIG Smile–I am Excited!
=============================================================
=========================================================

=========================================
============================================================
===============================================================
===========================
H33 (Beautiful Happiness)
==========================================================
=================================================
Question #4
The information technology department in a large organization is implementing a new system where the system allows, determines, and enforces various resources based on predefined company guidelines. Which concept is the department implementing?
A. Policy-driven access control
B. Authorization models
C. Zero trust
D. AAA
Question #5
Analyze and select the statement that accurately distinguishes the similarities between Mean Time to Repair (MTTR) and Mean Time Between Failures (MTBF).
A. MTTR is the median time it takes to correct a fault, while MTBF is the average time it takes to correct a fault.
B. The MTBF and MTTR calculations are the same.
C. Both MTTR and MTBF are for non-repairable assets.
D. Both MTTR and MTBF can determine the amount of asset redundancy a system should have.
Question #6
A system administrator at a medium-sized agency is working on improving the agency’s password management practices to enhance security. The admin wants to provide employees with efficient and secure ways to manage their passwords. As part of the implementation plan, the admin examines different password managers available in the market, each with unique features and capabilities. Which of the following are the advantages of using password managers for password management? (Select the two best options.)
A. Password managers can securely store and organize passwords for various online accounts and services.
B. Password managers can generate strong and complex passwords automatically, reducing the risk of weak passwords.
C. Password managers automatically use the same strong password for all stored accounts to reduce the complexity for users.
D. Password managers automatically synchronize passwords across competitors’ platforms to ensure seamless transition.
Question #7
A cyber technician pulls logs on the new Apple iMacs to ensure the company’s employees adhere to the policy. What log can provide the technician with the computer’s attempted logins or denial when an employee attempts to access a file?
A. Firewall logs
B. Endpoint logs
C. Application logs
D. Operating system-specific security logs
Question #8 ⭐ Missed During Our Practice
A company’s cybersecurity team evaluates threats that could exploit vulnerabilities in its physical infrastructure. The team is specifically considering threats that can directly harm the company’s systems and potentially damage data or services. What type of threat does this scenario BEST describe?
A. Network attacks
B. Social engineering attacks
C. Environmental threats
D. Downgrade attacks
Question #9
The IT security team at a corporation has concerns about potential security risks on the cloud platform. They noticed that some employees have been able to submit malformed data, leading to inconsistencies and potential data breaches. The team wants to enhance the platform’s security without hindering productivity. In this case, what security measure should the IT security team implement to improve the security of the cloud platform at the corporation?
A. Increase the number of login attempts before locking user accounts
B. Enable additional firewall rules to restrict employee access to the platform
C. Implement robust input validation mechanisms to validate all incoming data
D. Upgrade the cloud infrastructure to improve data processing speed
Question #10 ⭐ Missed During Our Practice
An organization is restructuring its IT governance framework to improve its cybersecurity strategy. The organization has several distributed offices across various geographical regions, each having a unique set of IT policies and infrastructure. The cybersecurity lead aims to increase control and consistency over the security practices in each office while retaining some autonomy for the individual offices to manage their specific risks. Which governance structure aligns with the objectives of the cybersecurity lead and effectively mitigates risks associated with the security practices at each office?
A. Decentralized governance with an executive committee
B. Centralized governance with an advisory board
C. Centralized governance with a steering committee
D. Change Control Board (CCB)
Question #11
The cybersecurity team at a software development firm is planning to enhance its deterrent controls to discourage potential cyber threats. Which of the following should the team implement?
A. Conducting regular security awareness training sessions.
B. Publicizing a successful prosecution of a cybercrime attempt.
C. Setting up an intrusion detection system (IDS).
D. Implementing a software patch management system.
Question #12
As a company grows, so does its attack surface and the desirability for a malicious actor to compromise its systems. A company must monitor all software usage, secure applications, third-party software, libraries, and dependencies to keep systems secure. What are some ways to accomplish this? (Select the three best options.)
A. Software composition analysis
B. Credentialed scan
C. Software Bill of Materials
D. Package monitoring
Question #13
An international e-commerce corporation is working to enhance its cybersecurity measures. It’s recently faced numerous advanced persistent threat (APT) attacks that have targeted specific vulnerabilities in their infrastructure. The board of directors has decided to focus on reducing the risk of similar attacks in the future. What approach should the corporation prioritize?
A. Opt for third-party cybersecurity services
B. Invest in more aggressive security measures
C. Focus on compliance with cybersecurity regulations
D. Adopt a defensive cybersecurity strategy
Question #14 ⭐ Missed During Our Practice
To improve security, the security team at a growing tech company aims to update its infrastructure. They explore different architecture models and ponder the implications of logical segmentation. To curb lateral movement within the network (in case an intruder accesses one segment), the team plans to split the network into smaller, isolated segments, each boasting its own resources and security controls. Considering this strategy to boost security, which architecture model would optimally support the logical segmentation strategy?
A. Client-server model
B. Peer-to-peer model
C. Monolithic model
D. Hybrid model
Question #15
A network engineer is optimizing an existing cloud-based system. The primary goal is to ensure the system remains operational, minimizing downtime, even under adverse conditions or potential failure points. What key characteristic of system design should the engineer prioritize?
A. Centralized
B. Availability
C. Containerization
D. Scalability
Question #16
A small enterprise wants to improve its network security. It uses a variety of switches, routers, and servers in its infrastructure. Which of the following practices should the enterprise primarily focus on to improve the security of these devices?
A. Implement secure baseline configurations and regularly update them
B. Physically move the servers to a different location every week
C. Use only wired connections and remove all wireless devices
D. Implement stronger break policies for the IT staff
Question #17
A cyber group is reviewing its web filtering capabilities after a recent breach. Which centralized web-filtering technique groups websites into categories such as social networking, gambling, and webmail?
A. Content categorization
B. Uniform resource locators (URL) scanning
C. Reputation-based filtering
D. Block rules
Question #18
After deploying a mobile device management system to all its computers, a company noticed a small subset failed to encrypt their hard drives. After inspection, those devices do not have the correct component required for the drive encryption to function. Which security component would the company need to install for the drive encryption to work?
A. RAM
B. CRL
C. TPM
D. CPU
Question #19
A multinational corporation wants to enhance its risk management procedures and validate that its systems, controls, and processes align with specific international standards, regulations, and best practices. Which approach should the organization consider to ensure an unbiased and comprehensive analysis of its security posture?
A. Internal audit
B. External examination
C. Self-assessment
D. Internal compliance assessment
Question #20
A system administrator has monitored several areas of the network and local systems that are out of their normal ranges. The administrator begins to believe they have caught a hacker on the network. Analyzing their activities on the network provides what information? (Select the three best options.)
A. Performance
B. Procedure
C. Tactic
D. Technique
Question #21 ⭐ Missed During Our Practice
A forensic analyst at an international law enforcement agency investigates a sophisticated cyber-espionage case. The analyst must uncover the timeline of document interactions, detect concealed or system-protected files, interpret categories of digital events, and trace digital breadcrumbs left behind during media uploads on social platforms. What combination of data sources would provide the MOST comprehensive information for this multifaceted investigation?
A. File metadata and event logs
B. File metadata with extended attributes and network transaction logs
C. Network transaction logs and gateway security logs
D. Event logs and gateway security logs
Additional Questions We Got Wrong
Question #35 ⭐ Missed During Our Practice
An acceptable use policy requires the system to encrypt confidential information while in transit. All employees must use secure email when exchanging proprietary information with external vendors. Which of the following describes this type of acceptable use policy?
A. Technical
B. Operational
C. Managerial
D. Preventive
Question #70 ⭐ Missed During Our Practice
A network engineer has the task of creating a remote access solution for a global enterprise. The solution should secure encrypted communication for the company’s employees worldwide and detect potential security threats in real time. Which configuration should the network engineer deploy to meet these requirements?
A. A network fortified by 802.1X port security, an Extensible Authentication Protocol (EAP), and a load balancer
B. A Software-Defined Wide Area Network (SD-WAN) with secure access service edge (SASE) implementation, supplemented by an intrusion prevention system (IPS)
C. A network equipped with a Next Generation Firewall (NGFW), a Web Application Firewall (WAF), and an intrusion prevention system (IPS) in tap/monitor mode
D. A VPN utilizing IKE and IPSec protocols, combined with an inline intrusion detection system (IDS)
Question #74 ⭐ Missed During Our Practice
A systems administrator receives an alert for potential unauthorized access to sensitive data while in active memory on a server within the organization. The organization has tasked the systems administrator with enforcing stricter controls to prevent such breaches. What would be the MOST appropriate measure to implement?
A. Data encryption
B. Permission restrictions
C. Data obfuscation
D. Data masking
Questions #84–90
Question #84 ⭐ Missed During Our Practice
A nonprofit organization with limited funds needs a cost-effective disaster recovery plan that doesn’t necessitate immediate resumption of services after a disaster. Which strategy is the MOST suitable?
A. Implement a hot site
B. Establish a COOP
C. Deploy a cold site
D. Set up a warm site
Question #85 ⭐ Missed During Our Practice
A growing company’s IT department is weighing the pros and cons of different architectural models for its next project. The debate narrows down to cloud architecture versus traditional network architecture. During a team meeting, the head of IT security asks a newly hired network specialist to identify the primary security consideration when comparing cloud architecture to traditional network architecture. Based on the conversation in the IT department, which security consideration is MOST directly associated with cloud architecture compared to traditional network architecture?
A. A need for regular network hardware/firmware updates
B. Encryption of data transmitted over local networks
C. Shared responsibility model with service providers
D. Requirement for secure physical access to network devices
Question #86 ⭐ Missed During Our Practice
A network engineer is segmenting a company’s network to improve security. In terms of routing infrastructure, which of the following strategies would the engineer employ to segment different types of hosts attached to the same switch?
A. Assign a different internet protocol (IP) address to each host on the switch.
B. Use the Address Resolution Protocol (ARP) to map each host’s IP interface to a different media access control (MAC) address.
C. Use the same VLAN IDs and subnets for all hosts.
D. Assign each host to a different virtual local area network (VLAN).
Question #87 ⭐ Missed During Our Practice
A hacker successfully exfiltrates a database of user passwords and attempts to gain access to it as the hacker can now go around the authentication system. What type of attack has the hacker achieved?
A. Dictionary
B. Password spraying
C. Offline
D. Brute force
Question #88 ⭐ Missed During Our Practice
A company wants to guarantee business continuity even if a catastrophic event occurs at its primary data center. What are the MOST appropriate strategies for the company to adopt? (Select the two best options.)
A. Deploy a warm site
B. Disperse locations geographically
C. Deploy a hot site
D. Utilize multicloud systems
Question #89 ⭐ Missed During Our Practice
A security analyst is reviewing server configurations in an organization during a vulnerability assessment. The analyst finds that someone left the default vendor passwords active on a critical server holding customer data. Additionally, someone is running unnecessary services on the server, and no one has patched it for several months. In this scenario, which vulnerability would adversaries MOST likely exploit first to gain unauthorized access to the critical server?
A. Absence of an intrusion detection system (IDS)
B. Use of open-source software
C. Default vendor passwords not changed
D. Non-encrypted data at rest
Question #90 ⭐ Missed During Our Practice
The IT department of a large organization plans to implement a mobile device management (MDM) solution to streamline device management and enhance security for its employees. The organization is considering two deployment models: Bring your own device (BYOD) and corporate-owned, personally enabled (COPE). Which deployment model allows the organization more control over mobile devices while still providing flexibility for employees to use their devices?
A. Hybrid deployment with limited cloud services access
B. Corporate-owned, personally enabled (COPE)
C. Bring your own device (BYOD)
D. A combination of Bring your own device (BYOD) and corporate-owned, personally enabled (COPE)

